In detail
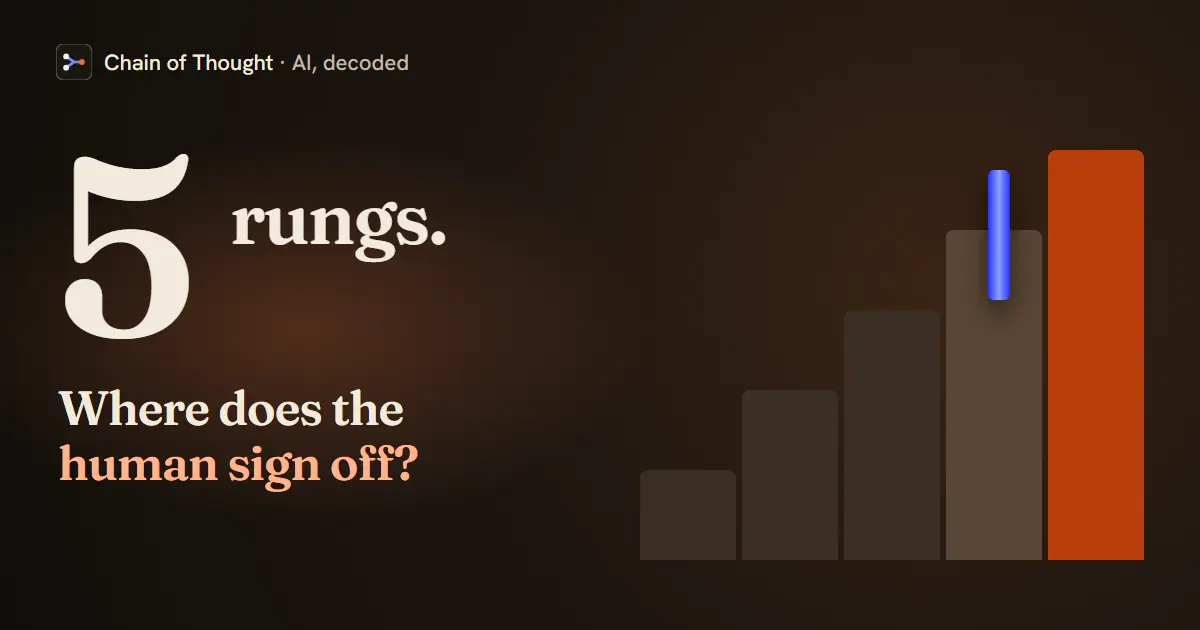
Aishwarya Srinivasan frames it through a coding copilot: do you let it write the code, review it, write the unit tests, push and merge? Walk those steps as a ladder; where each checkpoint belongs depends, she says, on your risk and compliance.
1. Write the code
The lowest-stakes rung. The agent drafts, you do everything else. Usually a safe handoff when a human reviews the result.
2. Review the code
Now it is checking work, not just producing it. Useful, and still low risk, because a human is downstream.
3. Write the tests
The agent decides what “correct” looks like. A bit more trust, because bad tests can hide real bugs.
4. Push the code
It is now taking an action with consequences outside its own sandbox. Depending on the risk, this is a natural place for a human checkpoint.
5. Merge to main
Full autonomy. With no approval step, the agent ships to the shared codebase with no one in between. Aishwarya’s warning: if you automate this entire chain and something breaks, you need to be able to trace back through every step to find where and why. Without logging and checkpoints along the way, she says, that becomes extremely hard.
If you do want a person at this rung, the tooling already exists. GitHub’s branch protection rules can require a set number of approving reviews and passing status checks before anything merges into a protected branch, and those rules apply to an agent’s pull requests the same as a person’s.
The same ladder, in general terms
The coding ladder is one instance of a general framework. In Levels of Autonomy for AI Agents, K. J. Kevin Feng, David McDonald and Amy Zhang define five levels by the role the person plays: operator, collaborator, consultant, approver and observer. They argue that autonomy is a design choice separate from how capable the agent is, so a very capable agent can still be deliberately run at a low level. Their levels don’t map one-to-one onto the rungs above, because they are defined by how the person interacts with the agent, not by which tasks it may do. The useful idea for the ladder is that separation: decide the person’s role at each rung on purpose instead of letting it follow from what the agent can do. Human in the loop vs. human on the loop covers the oversight side of that last step.
Why it matters
The autonomy question is not “how smart is the agent.” It is “how much does it cost if this step is wrong.” High-risk or regulated work earns a human in the loop. Low-risk work may not. Put the checkpoints where the risk is.
Hear it from the guest
“Do we let it write the code for me? Should I let it also review the code for me? Should I also let it write unit tests for me? Should I also let it push the code and like merge the code for me?”
“The level of autonomy versus the level of human intervention that you want to have in any particular system is very subjective to what's the level of risk that you have, what is the level of scrutiny or compliance that you're building that under.”
“The goal is defined and identified by the human and the means are delegated to the agent.”
“You're going to want to be more aggressive with sort of the adjacent stuff that's less dangerous and you're going to want to be a bit more careful with like your platform code or your DevOps environments”
Quotes lightly edited to remove filler words.
From the conversation
This explainer is drawn from these episodes — each carries its full transcript.